Singapore Jails Indian IT Lead Over Breach of 18,000 State Court Files
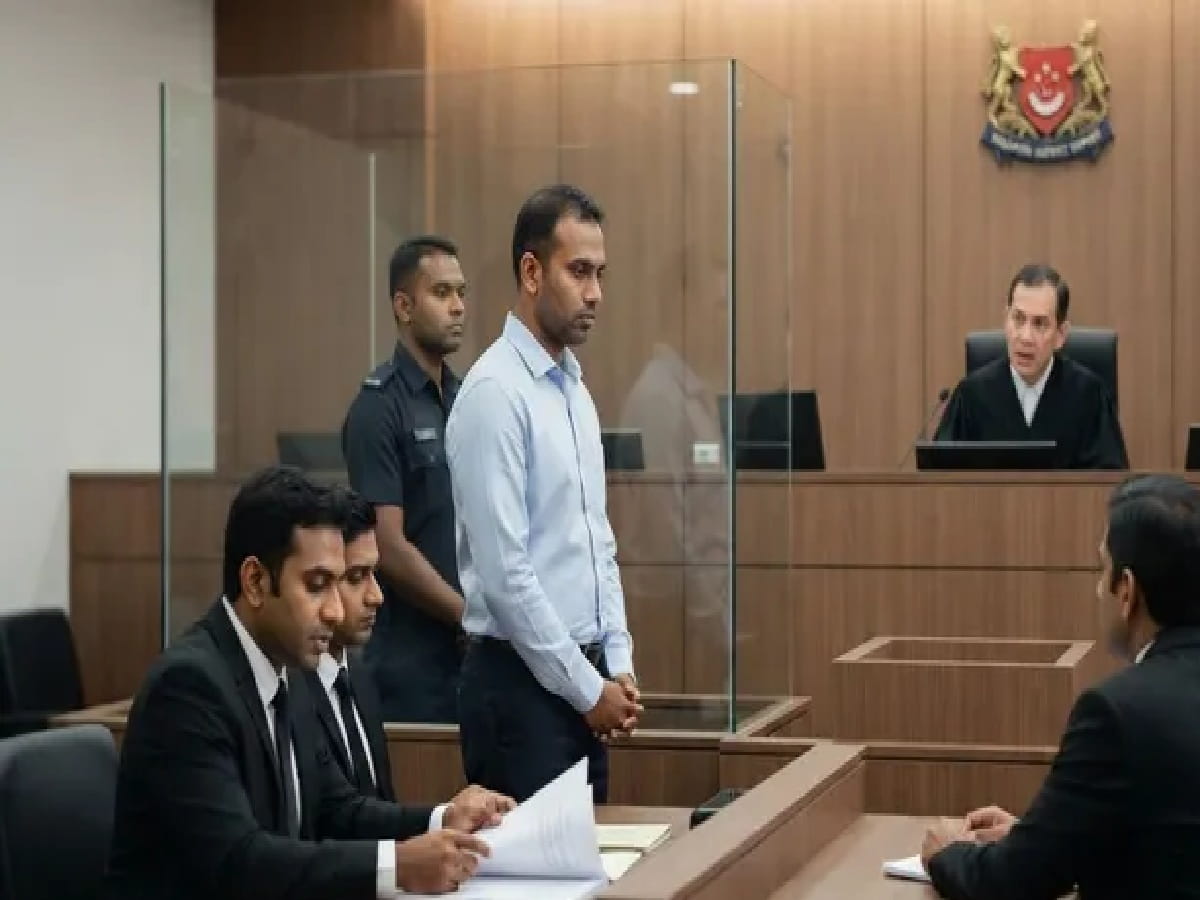
A Singapore district court has sentenced 42-year-old Indian national Janarthanan Tamil Kovan to 28 weeks (approximately seven months) of imprisonment after he severely compromised official digital security infrastructure, exposing more than 18,000 sensitive files tied to the Singapore State Courts. Janarthanan, who served as a Service Delivery Manager deployed through external technology vendor Lenovo PCCW Solutions, pleaded guilty to charges under the Official Secrets Act (OSA) alongside statutory violations regarding the unauthorized hacking and technical modification of a government-issued workstation. The judicial ruling follows an extensive investigation into how an authorized IT team lead charged with safeguarding public judicial systems bypassed fundamental protocol to grant remote control access to an external third party.
How a Certification Test Led to a Fatal Security Breach via Remote Desktop Tool
The breach originated on August 4, 2025, when Janarthanan attempted to take an online assessment for the globally recognized Certified Information Security Manager (CISM) credential. Because his personal computer was malfunctioning, he attempted to install and execute the examination software on his official court-issued Lenovo ThinkPad—a dedicated government device strictly governed by non-modification and access restrictions. When built-in administrative security locks prevented the test software from executing, Janarthanan reached out via WhatsApp to an acquaintance in India named Hari Balan. In direct violation of national security protocols, Janarthanan facilitated external remote access to the secured machine using an Indian IP address to bypass installation hurdles.
High-Risk Exposure of 18,016 State Files: Network Credentials and System Architecture Left Vulnerable
Forensic analysis by the Criminal Investigation Department’s (CID) Technical Crimes Branch revealed that at the moment remote desktop connectivity was established, the laptop housed 18,016 government files, including one classified under the highest sensitivity rating. The files contained administrative login credentials, secret cryptographic keys, and internal architectural maps of the judicial network. Although investigators confirmed that no direct file theft, extraction, or judicial case tampering occurred, the unauthorized access exposed the court network to potential backdoor exploitation, judge's internal records, and broader cyber intrusion risks. District Judge Loren Ho observed that granting an unvetted foreign entity control of a judicial system terminal posed catastrophic institutional risks, rejecting defense pleas for leniency and emphasizing that high-ranking cybersecurity leads must face firm accountability for deliberate compliance failures.